SMS Authentication for Online Accounts: Practical Security Guide
SMS Authentication for Online Accounts
A password may be the first line of defense for an online account, but it is not always enough on its own. People reuse passwords, forget them, choose weak combinations, or enter credentials into the wrong place. For businesses operating websites, apps, customer portals, and digital services, verifying that a user actually controls a particular phone number can add another useful layer to the authentication process.
That is where SMS authentication for online accounts comes in.
SMS authentication uses a temporary verification code, commonly called a one-time password or OTP, to confirm a user's identity or possession of a mobile number. It is familiar to most users and can fit naturally into registration, login, password recovery, and other verification workflows.
For businesses looking to implement this type of verification, a dedicated solution such as OTPGET can help simplify the process of incorporating SMS-based OTP verification into an application or service.
What Is SMS Authentication?
SMS authentication is a method of verifying a user by sending a temporary code to their mobile phone through SMS.
The basic idea is straightforward: instead of relying only on something the user knows, such as a password, the system can ask the user to enter a code delivered to a phone number associated with the account or verification process.
This temporary code is known as a one-time password. Unlike a static password, an OTP is intended for a specific verification attempt and generally expires after a limited period.
For example, imagine a customer creating an account on an online platform. After entering their phone number, they receive a message containing a short verification code. They enter that code into the website or application, and the system checks whether it matches the expected OTP.
If the verification succeeds, the application can continue with the relevant action.
How SMS Authentication Works
Although the underlying infrastructure can be technical, the user experience is usually simple.
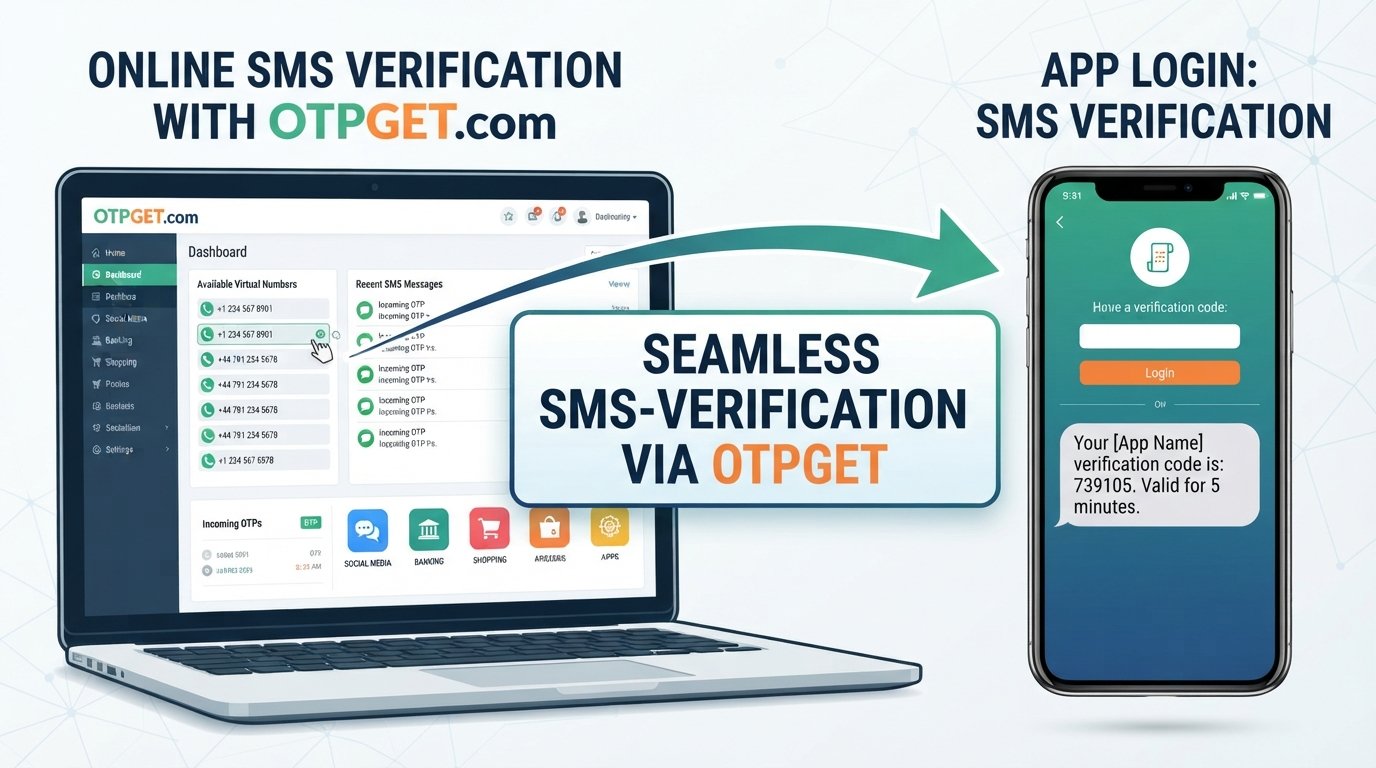
A typical SMS OTP verification workflow looks like this:
-
The user enters a phone number or login details.
The process begins when a user registers, logs in, resets a password, or performs another action requiring verification. -
The system generates a unique OTP.
The application creates a temporary one-time password for that verification request. -
The OTP is sent through SMS.
The verification code is delivered to the user's mobile number. -
The user enters the OTP.
The user types the received code into the relevant verification field. -
The system verifies the code.
The application checks whether the OTP is valid and associated with the current verification attempt. -
Access or the requested action is completed.
When verification succeeds, the application can allow the user to proceed.
This process can be used for both new-user verification and existing-account authentication.
Why Online Accounts Need Stronger Authentication
Passwords remain common because they are familiar and relatively easy to implement. However, password-only login creates several challenges for businesses and users.
Password reuse is one example. A person may use the same or similar password across multiple services. Weak or easily guessed passwords can create another problem. Forgotten credentials also contribute to account recovery requests and friction during login.
Businesses may additionally need to distinguish genuine users from automated or fraudulent registration attempts.
SMS-based verification can help address some of these challenges by adding a phone-number verification step to selected account workflows.
It can be particularly useful when a business wants to:
-
Verify that a user has access to a particular mobile number
-
Add another authentication layer to a login process
-
Confirm a new account during registration
-
Support account recovery
-
Verify a new device or sensitive action
-
Reduce reliance on password-only authentication
SMS authentication should not be treated as a complete security solution for every situation. The appropriate approach depends on the sensitivity of the account, the application's architecture, the expected threats, and the business's security requirements.
Benefits of SMS OTP Verification
One reason SMS OTP verification remains useful is its familiarity. Most users already understand the basic process of receiving a code and entering it into a website or app.
Simple user experience
There is little for users to learn. A verification message arrives, the user enters the code, and the process continues.
Mobile-based verification
SMS authentication allows businesses to verify access to a mobile number as part of registration or authentication workflows.
Additional account protection
An OTP can provide an additional verification step alongside a password or other authentication method.
Easier onboarding
Phone number verification can be incorporated into account creation without requiring users to install a separate authentication application.
Reduced dependence on static passwords
Because an OTP is temporary and generated for a particular verification attempt, it serves a different purpose from a permanent account password.
Flexible account workflows
Businesses can use SMS OTP verification for registration, login, password recovery, new-device verification, and selected sensitive actions.
Common Use Cases for SMS Authentication
SMS authentication can support many types of digital services.
User registration: A website can ask new users to verify their phone number before completing account creation.
Login verification: Businesses can use an OTP as an additional step during selected login workflows.
Two-factor authentication: SMS can serve as one factor in a broader 2FA process, depending on the application's design.
Password reset: A temporary code can help verify a user's access to the phone number associated with an account.
New-device verification: A business may request additional verification when a user signs in from a new device.
Transaction confirmation: Digital services can use OTPs to confirm certain user-initiated actions.
Account recovery: SMS verification can form part of an account recovery workflow.
Customer portals and e-commerce: Online stores, customer dashboards, and business applications can use phone number verification to support account management.
Fintech and digital services: Services handling account information or digital transactions may incorporate additional verification steps, subject to their own security, legal, and operational requirements.
The important point is that OTP authentication is not limited to login screens. It can become part of a broader user verification strategy.
SMS Authentication vs Password-Only Login
Password-only authentication and SMS OTP authentication serve different roles.
With password-only authentication, the user provides a credential they have previously created. The system checks that credential against the account.
With SMS OTP authentication, the system introduces a temporary verification code delivered to a registered or provided mobile number.
A simplified comparison looks like this:
| Approach | Typical verification method | Common consideration |
|---|---|---|
| Password only | Static password | Simple, but depends heavily on password security |
| SMS OTP | Temporary code sent by SMS | Adds a mobile-based verification step |
| Password + SMS OTP | Password followed by OTP | Adds another layer to the login workflow |
SMS authentication can improve the depth of a verification workflow, but SMS itself has security considerations. Phone-number takeover, social engineering, compromised devices, and other attack scenarios mean businesses should consider SMS OTP as one component of a broader account-security strategy rather than a universal solution.
What Is an SMS OTP API?
An SMS OTP API allows an application to communicate with an OTP or messaging service programmatically.
Instead of manually handling every part of the verification process, an application can send a request to an authentication service when an OTP needs to be generated or delivered.
A typical workflow might involve:
-
The application requests an OTP for a user's phone number.
-
The OTP service handles the verification request.
-
The code is delivered through SMS.
-
The user submits the code through the application.
-
The application or verification service checks the submitted OTP.
-
The result determines whether the user can continue.
An SMS verification API, OTP verification API, or broader authentication API can therefore become an important connection between a business's application and its verification workflow.
For many businesses, using an existing OTP service can be more practical than building every component internally, particularly when the team wants to focus its engineering resources on the core product.
Why Businesses Use OTPGET for SMS Authentication
Implementing SMS-based authentication involves more than adding a text field to a login page. Businesses need a workflow for requesting verification, handling OTPs, delivering messages, checking submitted codes, and managing situations such as expired or unsuccessful attempts.
This is where a dedicated solution such as OTPGET can be considered.
OTPGET can help businesses incorporate SMS OTP verification into their user-verification and authentication workflows without requiring them to build the entire verification process from scratch.
Depending on the application's requirements, businesses can use an OTPGET-based approach to support workflows such as:
-
Phone number verification
-
New-user account verification
-
SMS OTP authentication
-
Login verification
-
Password recovery workflows
-
User verification for digital services
-
Additional verification for selected account actions
The practical advantage of using a dedicated OTP solution is reduced technical complexity around the verification workflow. Instead of treating OTP functionality as an isolated feature, a business can incorporate it into the broader account journey.
For product teams and developers, the key question is not simply whether SMS authentication exists. It is whether the chosen service fits the application's verification requirements, technical architecture, user experience, and operational needs.
OTPGET is one solution businesses can explore when SMS-based OTP verification is part of that requirement.
How to Choose an SMS Authentication Service
Choosing an SMS authentication service should involve more than comparing a list of features. The service needs to fit the way your application actually handles users and authentication.
Consider the following factors:
API availability
Look for an API approach that can connect naturally with your application's authentication workflow.
Ease of integration
The implementation process should be understandable for the developers responsible for connecting verification to your application.
OTP delivery
Consider how the service handles OTP delivery and whether its capabilities align with the locations and users you need to support.
Verification workflow
Understand how OTP requests, verification attempts, expiration, retries, and failed attempts are handled.
Documentation
Clear documentation can make implementation and troubleshooting considerably easier.
Scalability and reliability
Consider whether the service can support your expected verification volume and operational requirements as your user base changes.
Security practices
Review how sensitive verification data is handled and what security controls are available.
Monitoring and reporting
Visibility into verification activity can help teams identify delivery or authentication issues and investigate unusual activity.
Cost and support
Evaluate the overall cost structure and the level of technical or customer support available for your business.
These criteria can also be used when evaluating OTPGET against the specific needs of your application.
Best Practices for SMS OTP Authentication
A well-designed OTP workflow should account for both usability and security.
Use short-lived OTPs. Verification codes should not remain valid indefinitely.
Limit verification attempts. Attempt limits can help reduce repeated guessing against a verification request.
Apply rate limiting. Restrict excessive OTP requests to help prevent abuse and unnecessary message traffic.
Avoid predictable codes. OTP generation should use an appropriate mechanism rather than simple predictable sequences.
Protect sensitive information. Do not expose OTPs unnecessarily in URLs, application logs, analytics systems, or error messages.
Use secure API communication. Authentication-related communication between application components should use appropriate secure transport and access controls.
Give users clear messages. Tell users when a code has expired, when they can request another one, or when verification has failed.
Handle expiration gracefully. A user who enters an expired OTP should have a clear path to request a new verification code.
Monitor suspicious activity. Repeated requests, unusual verification patterns, or excessive failed attempts may warrant additional controls.
Provide appropriate recovery methods. Account recovery should be designed carefully so that the recovery process does not undermine the security of the original authentication method.
These practices help make SMS-based authentication more dependable without treating it as a perfect defense against every account-security threat.
Is SMS Authentication Right for Your Online Account?
There is no single authentication method that fits every online service.
The right approach depends on factors such as account sensitivity, user expectations, threat model, business requirements, and technical architecture.
For many websites and applications, SMS authentication can be a practical way to verify mobile numbers and add an additional step to selected account workflows. It can also provide a familiar experience for users who are already accustomed to receiving verification codes by text message.
For businesses planning to introduce SMS OTP verification, a dedicated service can simplify the implementation journey.
OTPGET can be explored as a practical solution for businesses that need SMS-based user verification and OTP authentication workflows. Whether the goal is account registration, login verification, phone number verification, password recovery, or another verification use case, the right implementation starts with a clear understanding of the application's requirements.
FAQ: SMS Authentication for Online Accounts
What is SMS authentication?
SMS authentication is a verification method that sends a temporary code to a user's mobile phone. The user enters the code into an application or website, allowing the system to verify access to the provided phone number.
How does SMS OTP verification work?
A system generates a one-time password and sends it to the user's phone through SMS. The user enters the code, and the system checks whether it is valid for the current verification request.
Is SMS authentication the same as two-factor authentication?
Not always. SMS authentication can be used as part of two-factor authentication when combined with another authentication factor, such as a password. SMS OTP can also be used independently for phone number or account verification.
What is an OTP verification API?
An OTP verification API provides a programmatic way for an application to request, deliver, and/or verify one-time passwords. It can connect an application's account workflow with an OTP verification service.
Why do websites use SMS verification?
Websites may use SMS verification to confirm a user's mobile number, support account registration, add a verification step to login, assist with password recovery, or confirm selected account actions.
How can businesses implement SMS authentication?
Businesses can integrate an SMS verification or OTP service into their application's authentication workflow. The implementation typically involves requesting an OTP, delivering it to the user, accepting the submitted code, and verifying the result.
What is an SMS OTP service?
An SMS OTP service provides infrastructure or functionality that helps businesses deliver and verify one-time passwords through SMS. It can reduce the need to build the complete OTP workflow internally.
Can OTPGET be used for SMS authentication?
OTPGET can be explored by businesses looking to implement SMS OTP verification and SMS-based authentication workflows. The appropriate use depends on the application's specific verification requirements and implementation needs.
Final CTA
If your business needs a practical way to add SMS OTP verification to user registration, login, phone number verification, or other account workflows, OTPGET is worth exploring as part of your authentication strategy.
Evaluate your verification requirements, identify the workflows that need an additional layer of user verification, and consider how OTPGET can fit into your application's authentication process.